Windows Offensive - TryHackMe 10 writeup
Dieci room TryHackMe completate tra agosto e settembre. Trattate vulnerabilità note su host, su Active Directory, con un plus sull'analisi post compromissione (le tracce che un attaccante lascia dietro di sè)
writeups▾
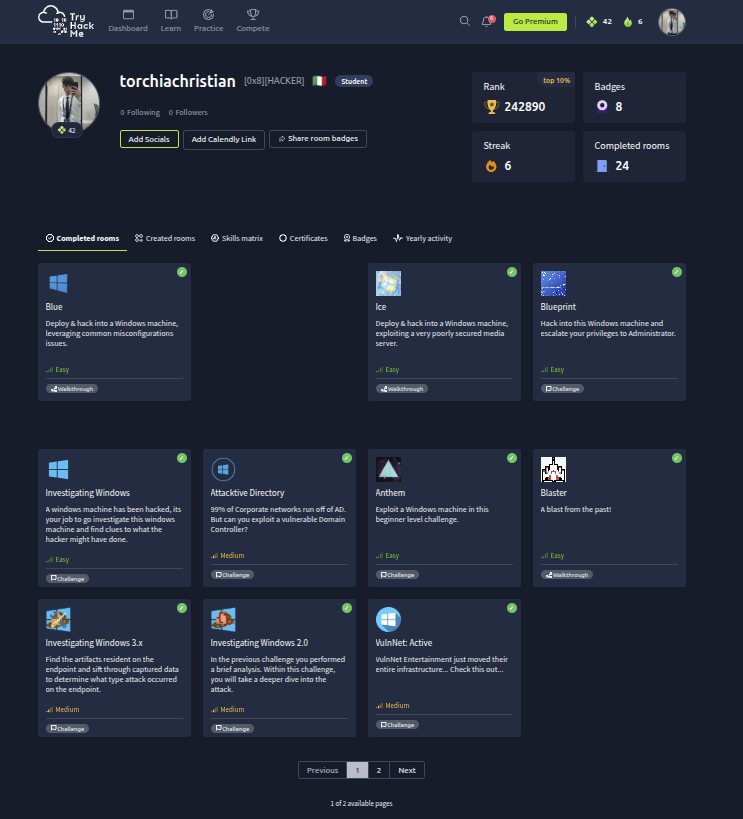
VulnNet: Active THM
Domain Controller con le porte AD filtrate e un Redis 2.8 esposto. Lettura file arbitraria via Lua, hash NetNTLMv2 catturato con Responder, SYSTEM con GodPotato.
Macchina già compromessa, sedici domande investigative. Webshell .jsp, mimikatz rinominato, tre meccanismi di persistenza e hosts file avvelenato.
Due attacchi diversi sulla stessa macchina: una backdoor agganciata al servizio di stampa di Windows, e il framework Empire nascosto dentro explorer.exe, il processo del desktop.
Trenta domande su una macchina compromessa. L'attaccante ha lasciato una backdoor WMI che chiama casa ogni ora e che chiude Process Explorer appena provi ad aprirlo.
Blueprint THM
osCommerce con la directory install mai rimossa. Nessun payload PHP regge sul target: la strada è php/exec più un eseguibile msfvenom servito via HTTP.
L'accesso iniziale passa da Kerberos stesso: kerbrute, AS-REP roast su svc-admin, credenziali base64 in una share backup, DCSync e pass-the-hash.
Anthem THM
Nessun exploit, solo osservazione richiesta. Password nel robots.txt, username ricavato da un documento, privilege escalation riscrivendo le ACL di una cartella.
Ice THM
RCE su Icecast, bypass UAC per arrivare a SYSTEM, dump di SAM e LSA secrets con kiwi.
Blue THM
EternalBlue su SMB. Il payload reverse_tcp viene bloccato in uscita, bind_tcp apre una shell diretta come SYSTEM.
Blaster THM
WordPress nascosto sotto /retro, credenziali nei commenti di un post, escalation a SYSTEM via CVE-2019-1388 sulla finestra UAC di hhupd.exe.
Kaspersky{CTF} 2026 3 writeup
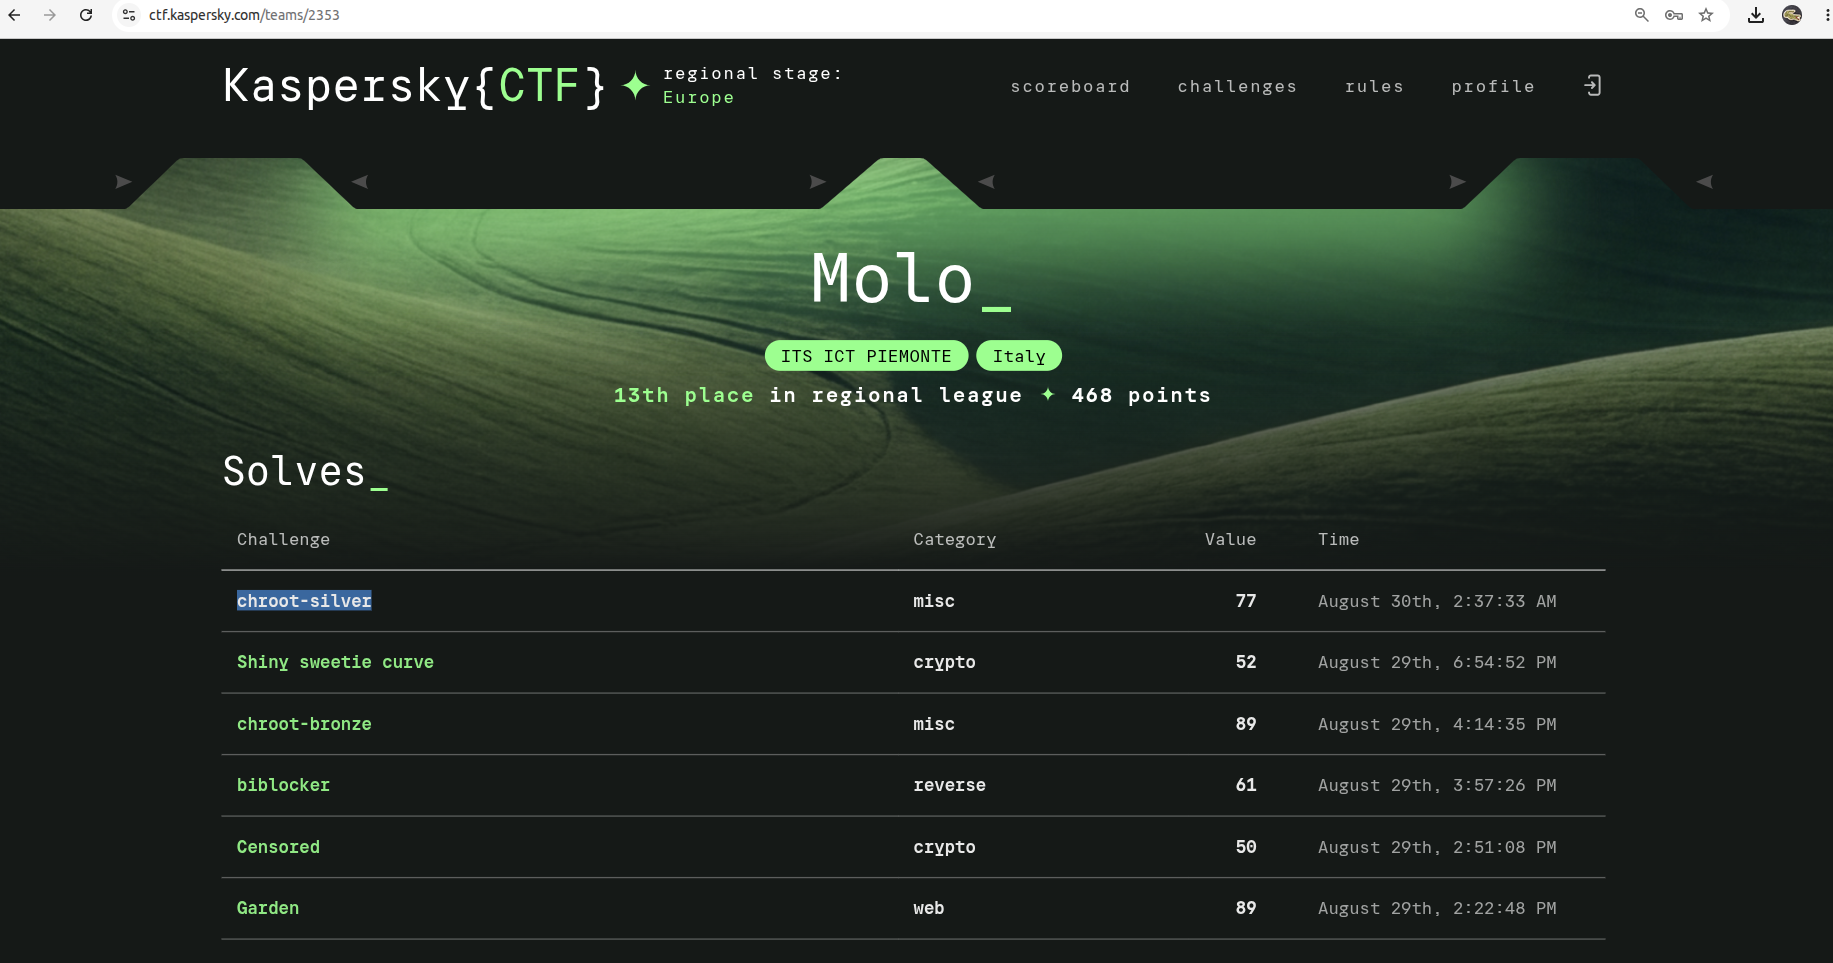
Lega regionale Europea con competizione a squadre: partecipato con team MOLO dell'ITS ICT Piemonte. Chiusa al 13esimo posto con 553 punti e 9 challenge completate dalla squadra. Qui ci sono i writeup di quelle risolte da me.
writeups▾
Sudokrypt KCTF
53 punti. Il servizio cifra qualunque cosa gli mandi, e la flag te la dà solo cifrata. Con 96 tentativi si ricostruisce il generatore di chiavi, che non è casuale come sembra, e si decifra.
Cimple KCTF
83 punti. Un eseguibile .NET che dentro ne nasconde altri tre, fra cui un finto processore con istruzioni inventate. La password non è scritta da nessuna parte: si ricava al contrario dai 16 controlli che il programma fa.
chroot-silver KCTF
77 punti. La shell parte dentro un chroot con due sole directory e nessun comando. Ma /bin/sh è BusyBox, che contiene mount e tutto il resto: si monta /proc e da lì si esce dalla gabbia.
HackTheBox 3 writeup
Macchine singole, catena di attacco completa: enumerazione, exploitation, privilege escalation.